Domain Security & Recovery
Real-world domain disasters and the controls that stop them — hijacking, DNS takeovers, key management, and recovery.
- Registrar lock
- DNS hardening
- Key custody
- Recovery plan
Domain Hijacking vs DNS Hijacking: How Attacks Happen
Understand how domain and DNS hijacking happen, where control can be lost, and which protections address the common attack paths.
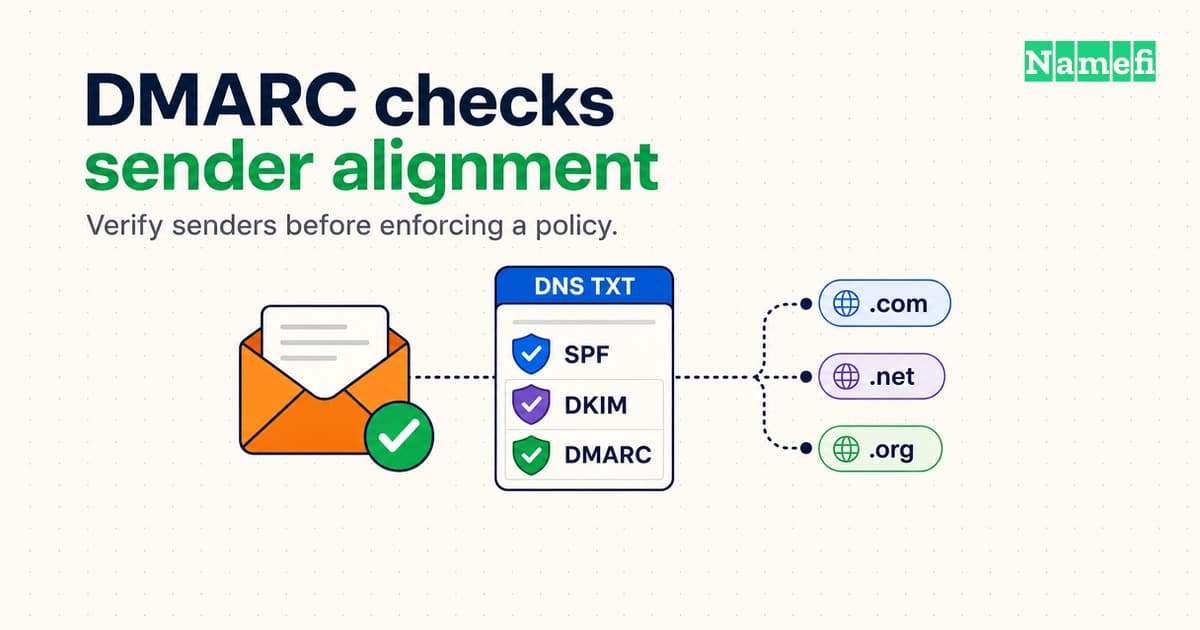
DMARC Records Connect Sender Alignment to Mail Handling
Create and check a DMARC TXT record, distinguish authentication from alignment, and review reports before enforcing quarantine or rejection.
The eMudhra CA Compromise Shows Why Domain Security Needs More Than HTTPS
Understand the eMudhra CA key compromise, website impersonation risks, and the different protections from DNSSEC, DANE, CAA, and CT.
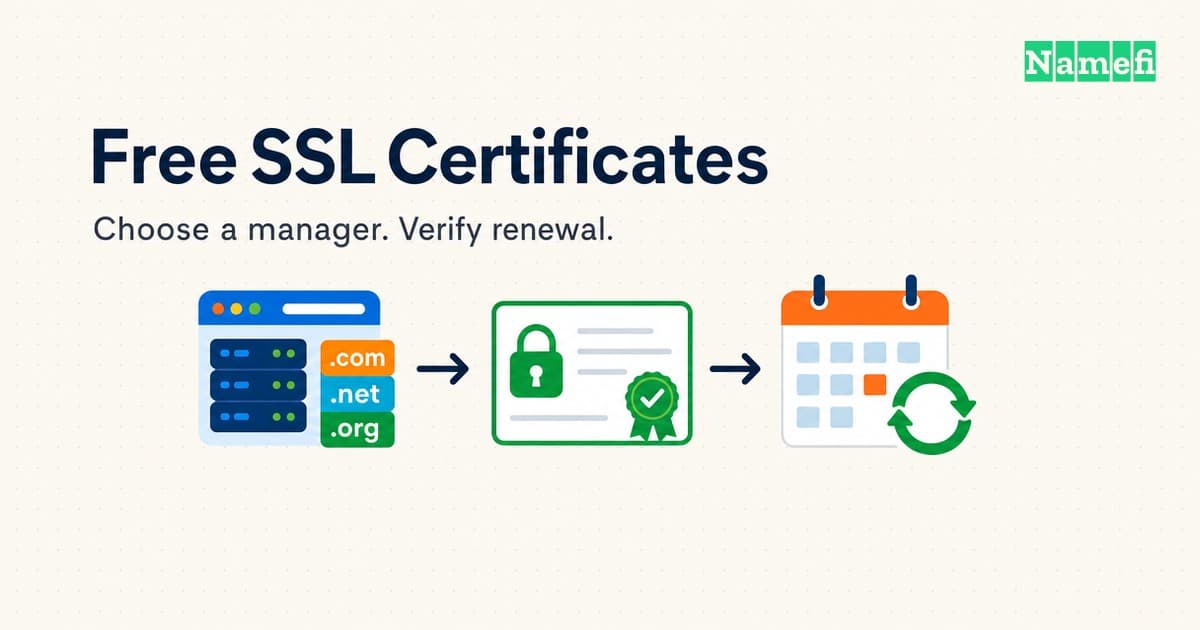
A Free SSL Certificate Still Needs Reliable Deployment and Renewal
Get a free TLS certificate through managed hosting or Let's Encrypt. Check domain control, hostname coverage, deployment, and renewal responsibility.
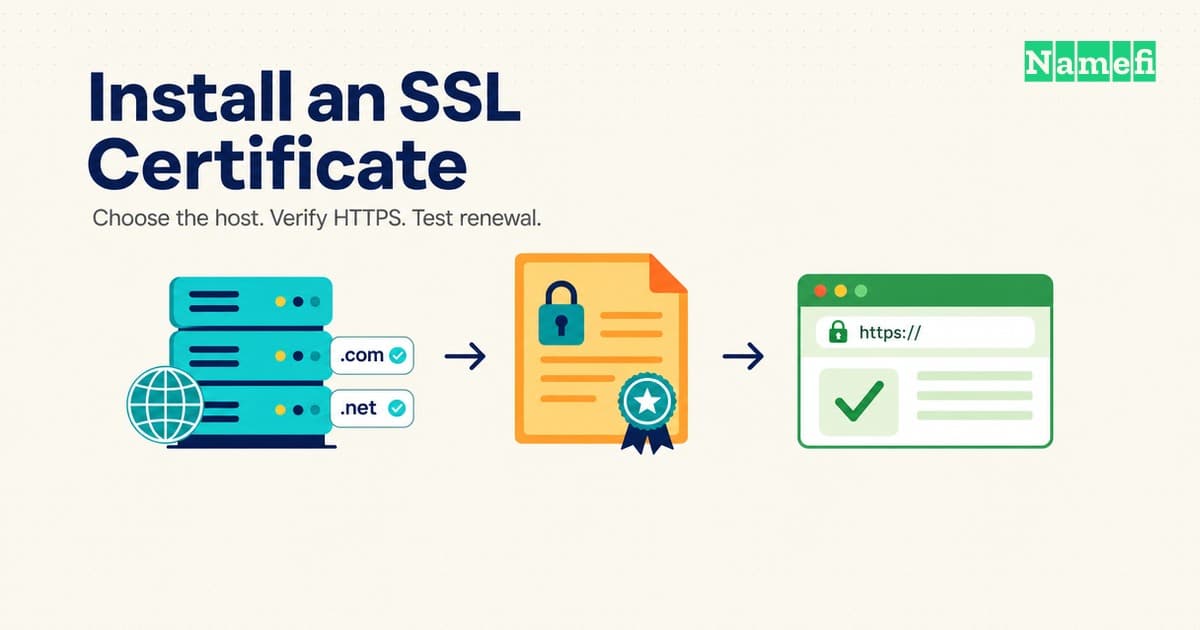
How to Install an SSL Certificate and Check HTTPS
Install an SSL certificate through your host or Certbot, choose domain validation, check HTTPS, and test automatic renewal.
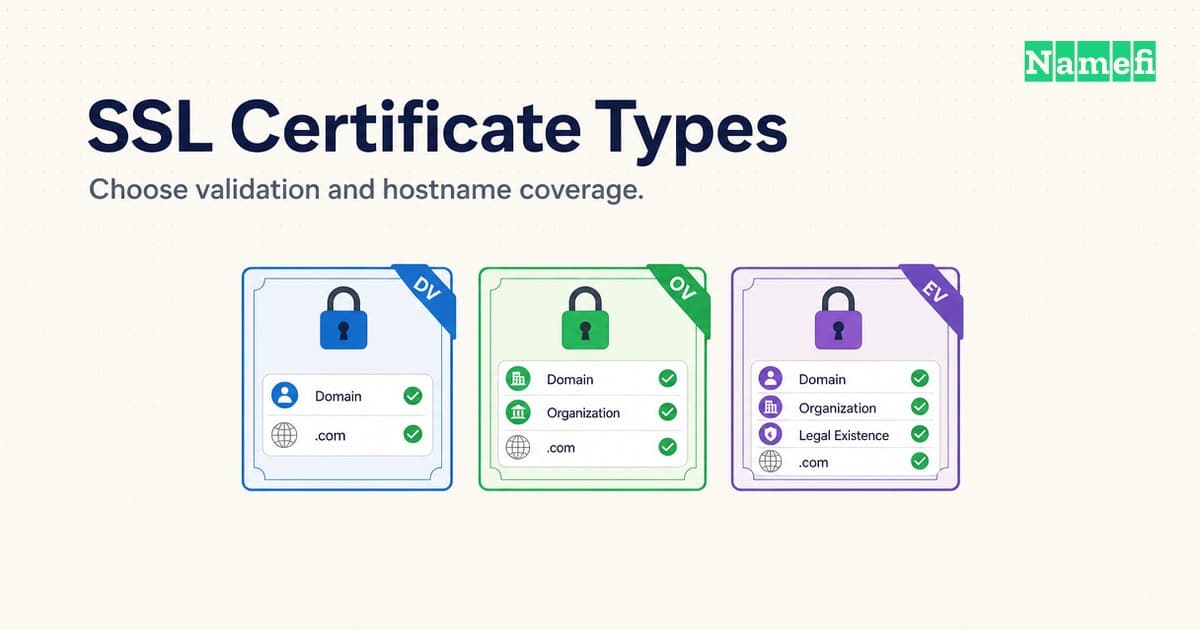
SSL Certificate Types Answer Different Identity and Coverage Needs
Compare DV, OV, EV, wildcard, and multi-domain TLS certificates. Choose identity checks and hostname coverage separately.
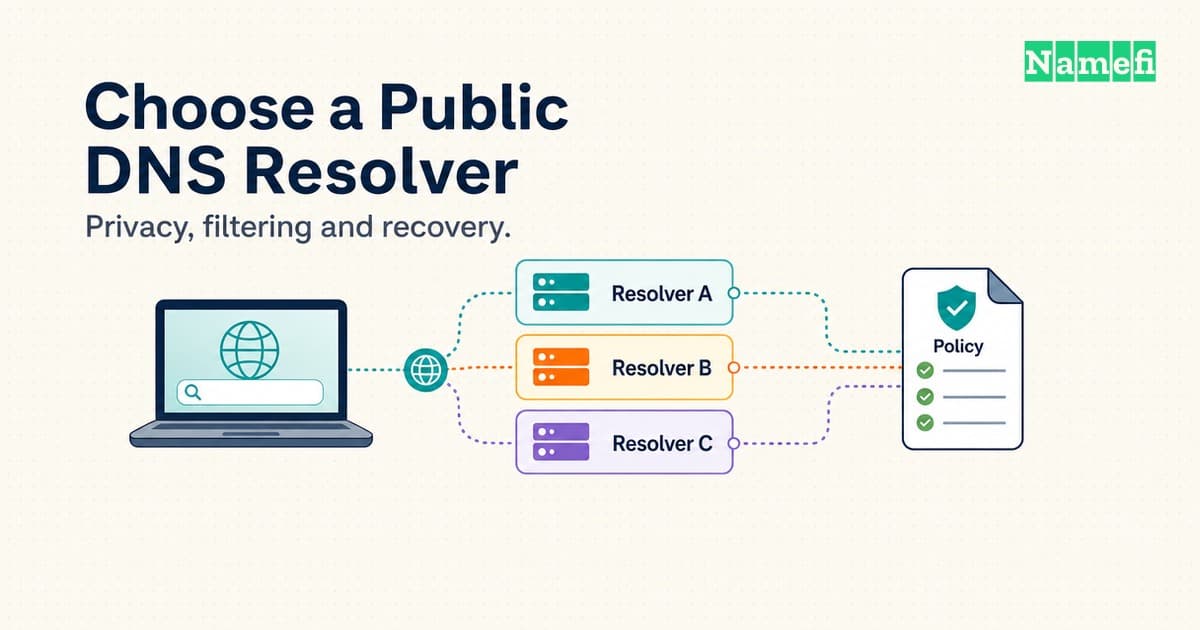
A Public DNS Resolver Should Match Your Privacy and Recovery Needs
Choose a public DNS resolver by privacy, DNSSEC, filtering, and recovery behavior, then test the settings your devices actually use.
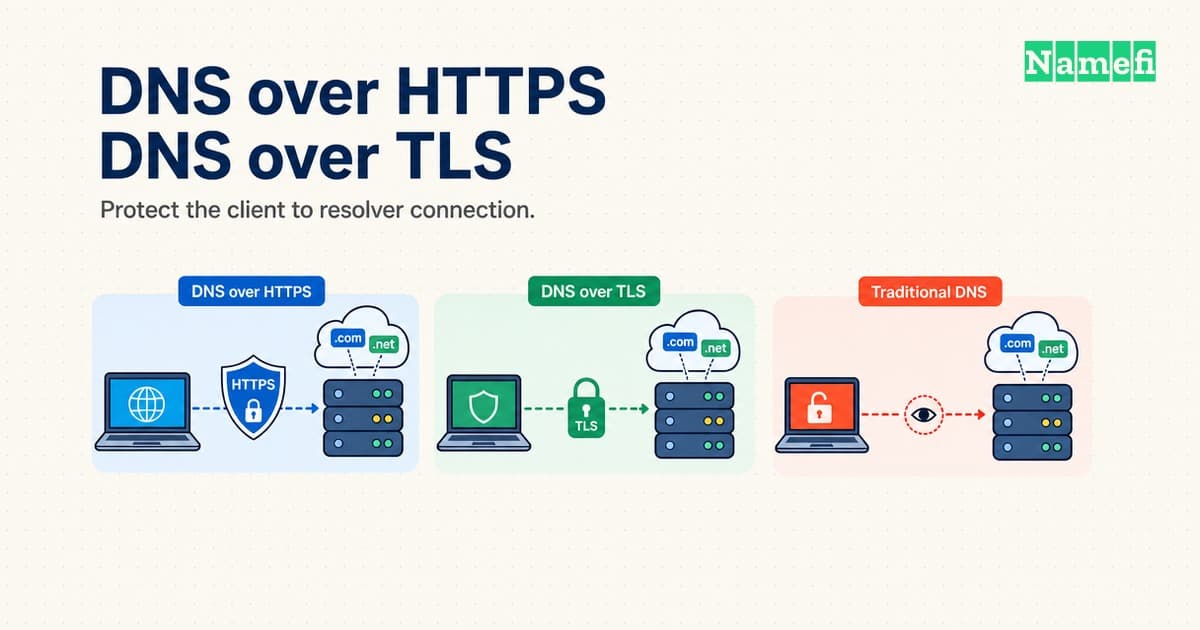
DNS over HTTPS and DNS over TLS protect the resolver connection differently
Compare DoH and DoT ports, authentication, fallback, and privacy limits, then verify which DNS connection your device actually uses.
Domain Privacy Hides Contact Details While Proxy Services Change the Registrant
Compare domain privacy, proxy registration, and RDAP redaction, then check disclosure terms, contact forwarding, and account recovery.
DNS Glue Records Give Resolvers a Nameserver Address
Understand parent-side DNS glue, compare in-domain and sibling nameservers, and verify safe glue changes with parent and child queries.
A Registrar Account Needs Strong Login and Independent Recovery
Harden a registrar account with phishing-resistant login, recovery planning, limited access, transfer controls, and reliable renewal checks.
SSL Certificate Renewal Requires Validation and Deployment Checks
Renew a TLS certificate, preserve domain validation, automate deployment, and check the certificate that visitors actually receive.
DNS TTL Explains Cache Timing During a Record Change
Plan DNS changes with TTL, distinguish cached and authoritative answers, and diagnose negative caching, stale data, and migration delays.
HTTP vs HTTPS: Encryption, Certificates, and How HTTPS Works
Compare HTTP and HTTPS, then learn how TLS encryption, certificates, ports, and automated certificate renewal protect web connections.
The Cat-and-Mouse War of Email Sender Reputation
A source-backed history of the thirty-year arms race over email sender reputation—the open relays, botnets, image spam, snowshoe campaigns, warmup networks, and other tricks bulk senders used to look trustworthy, the named operators who ran them, and the year and mechanism by which each trick was detected and shut down.
Onchain Domain Custody, Wallets, and Recovery
How custody really works for onchain domains: wallets, multisig, seed-phrase risk, and recovering a tokenized domain after wallet loss.
How to Avoid Domain Sale Scams
The common domain-sale scams — fake escrow, fake buyers, overpayment chargebacks, transfer-before-payment — and the habits that keep your sales safe.
Cybersquatting vs Legitimate Domaining: UDRP and ACPA Explained
Where legitimate domaining ends and cybersquatting begins: the UDRP three-part test, the ACPA, reverse domain hijacking, and how to stay safe.
Domain Flipping and the Law: Trademarks, UDRP, and Scams
The legal landscape every domain flipper needs: trademark basics, UDRP and ACPA, escrow at closing, hijacking defense, and how to dodge sale scams.
The $12 Minute: When Google Domains Accepted a Google.com Order
In September 2015, Google Domains accepted a $12 order for google.com from former employee Sanmay Ved, then canceled it about a minute later. What the incident proves, what remains uncertain, and why the $6,006.13 bounty still matters for domain security.
Domain Mayday EP03: The 2020 Twitter Bitcoin Account Takeover
On July 15, 2020, attackers phoned their way into Twitter, hijacked the verified accounts of Obama, Biden, Musk, Gates, Apple and Uber, and ran a Bitcoin doubling scam — netting about $118,000. A deep-dive on how control of an online identity was stolen, and what it teaches about owning a name.
Domain Mayday EP05: The 2024 Squarespace DeFi Domain Mass-Hijack
In July 2024, a registrar migration from Google Domains to Squarespace turned weak default authentication into a mass attack surface. Attackers hijacked the domains of crypto and DeFi projects — Compound Finance, Celer Network, Pendle, Unstoppable Domains — and pointed them at wallet-drainer phishing sites. Here is how a "seamless" migration created hundreds of unlocked front doors, and what it teaches about registrar security and MFA.
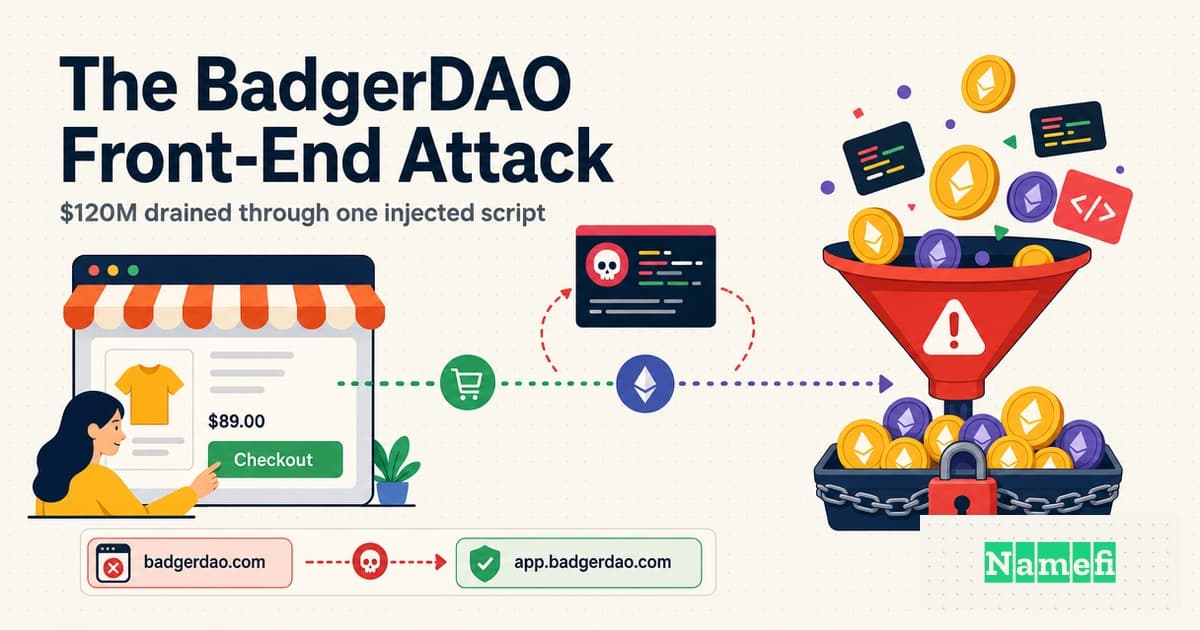
The BadgerDAO Front-End Attack: $120M Drained Through One Injected Script
In December 2021, attackers compromised BadgerDAO's Cloudflare account and injected one malicious script into its website front-end. The audited smart contracts were never touched — yet ~$120M walked out the door through wallet approvals users signed without knowing. A deep-dive on why the website is part of your security surface.
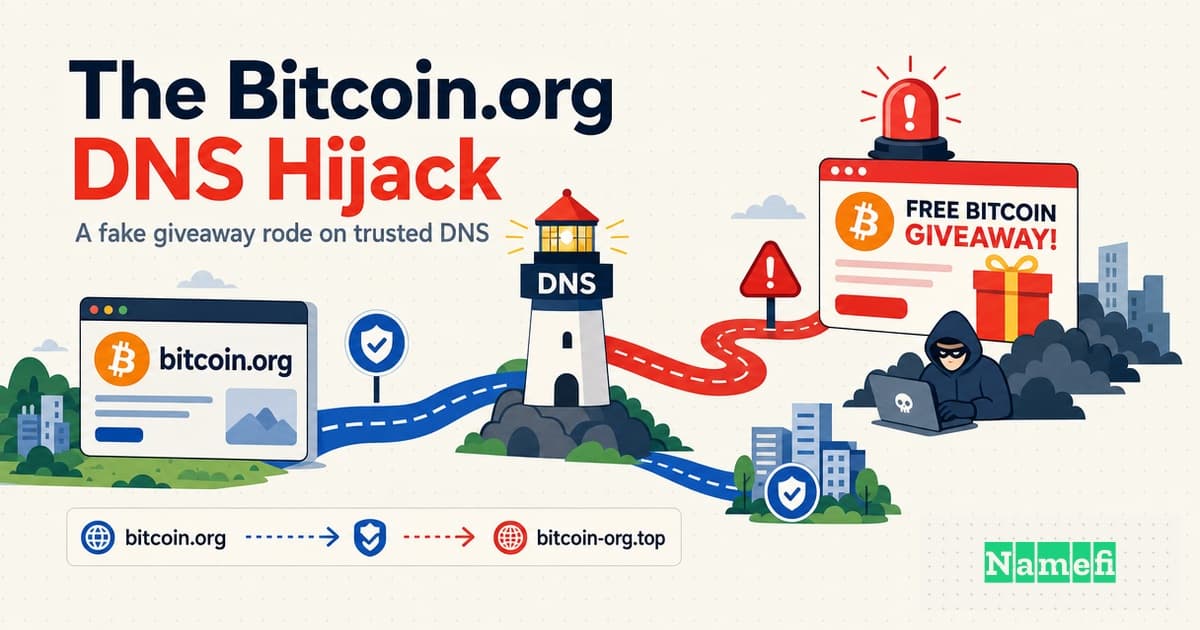
The Bitcoin.org Website Hijack: How Bitcoin's Home Page Became a "Double Your Coins" Scam
In September 2021, Bitcoin.org — the long-time informational home of Bitcoin run by the pseudonymous operator Cobra — displayed a fake "double your Bitcoin" giveaway before the site was pulled offline. Nameserver and WHOIS changes led observers to suspect DNS compromise, but the public root cause remained unconfirmed. Here is what the incident teaches about crypto-native sites depending on ordinary domain infrastructure.
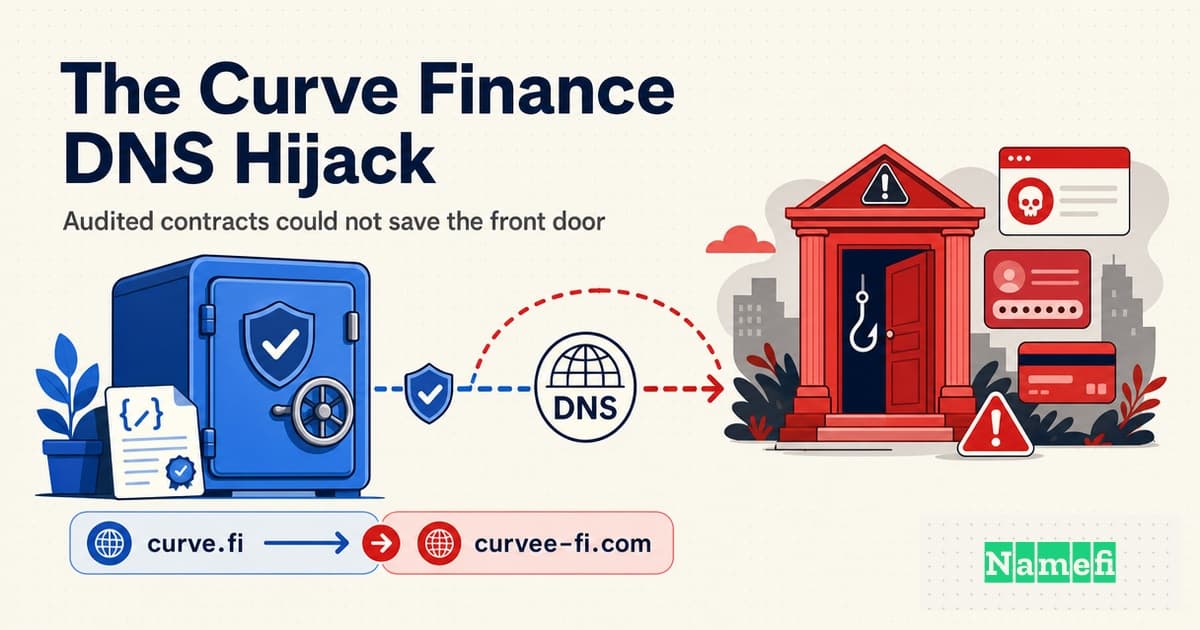
The Curve Finance DNS Hijack: When "Audited Contracts" Couldn't Save the Front Door
In August 2022, Curve Finance's smart contracts were untouched — but attackers hijacked the curve.fi domain at its registrar, cloned the site, and drained roughly $570K from users. A deep-dive into the DNS attack on a DeFi front-end, and what it teaches about domain security.
DNSpionage: The Campaign That Weaponized DNS Against Governments
In late 2018, Cisco Talos disclosed DNSpionage — a campaign later linked by researchers to Iranian interests that included malware and a separate DNS-redirection operation against government and company domains. In January 2019, CISA ordered federal agencies to audit and secure DNS infrastructure through Emergency Directive 19-01.
The Dyn DNS Attack: When a Mirai Botnet Disrupted Major Internet Services
On October 21, 2016, a DDoS attack powered by the Mirai IoT botnet hit DNS provider Dyn in three waves, making Twitter, Netflix, Reddit, Spotify, GitHub, Airbnb, PayPal, and other services unreachable for many users — a Domain Mayday case study in DNS provider concentration.
Domain Mayday EP14: When a Security Firm Got DNS-Hijacked — The Fox-IT Incident
In September 2017, attackers logged into Dutch security firm Fox-IT's third-party domain registrar, changed its DNS, fraudulently obtained a TLS certificate, and ran a 10-hour man-in-the-middle on client traffic — until Fox-IT caught it and published one of the most transparent post-mortems in the industry.
The GoDaddy Multi-Year Campaign: Hosting Breaches, Exposed Credentials, and Malicious Redirects
GoDaddy says hosting incidents disclosed between 2020 and 2022 were part of a multi-year threat campaign that exposed 1.2 million Managed WordPress customers and redirected some hosted websites. A close look at provider concentration risk — and at what the disclosures do not establish.
When ICANN Staff Got Phished: The 2014 CZDS Data Breach
In late 2014, spear-phishing emails spoofing ICANN's domain harvested staff credentials and enabled administrative access to files in the Centralized Zone Data System. A close look at the copied gTLD zone data and user information that were exposed — and the critical IANA systems that were not affected.
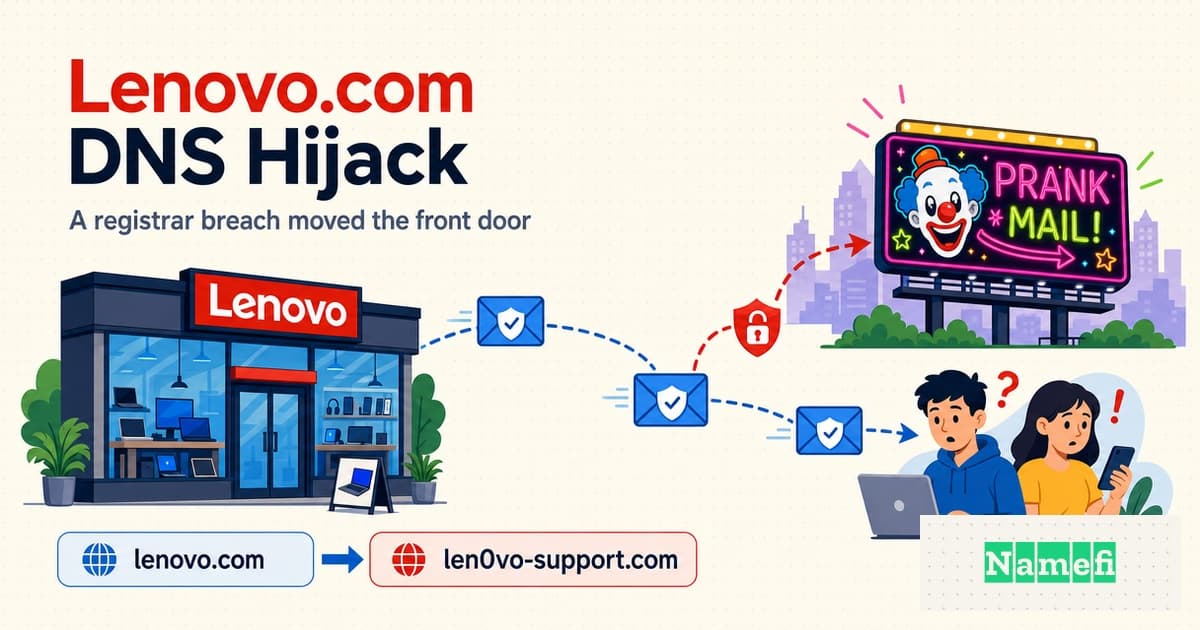
The Lenovo.com DNS Hijack: When Lizard Squad Took a Hardware Giant's Front Door
On February 25, 2015, attackers changed Lenovo.com's nameserver and mail routing, sending visitors to a webcam slideshow and exposing some email traffic. Researchers attributed the incident to a Webnic compromise, but Webnic did not publicly confirm their reported exploit chain.
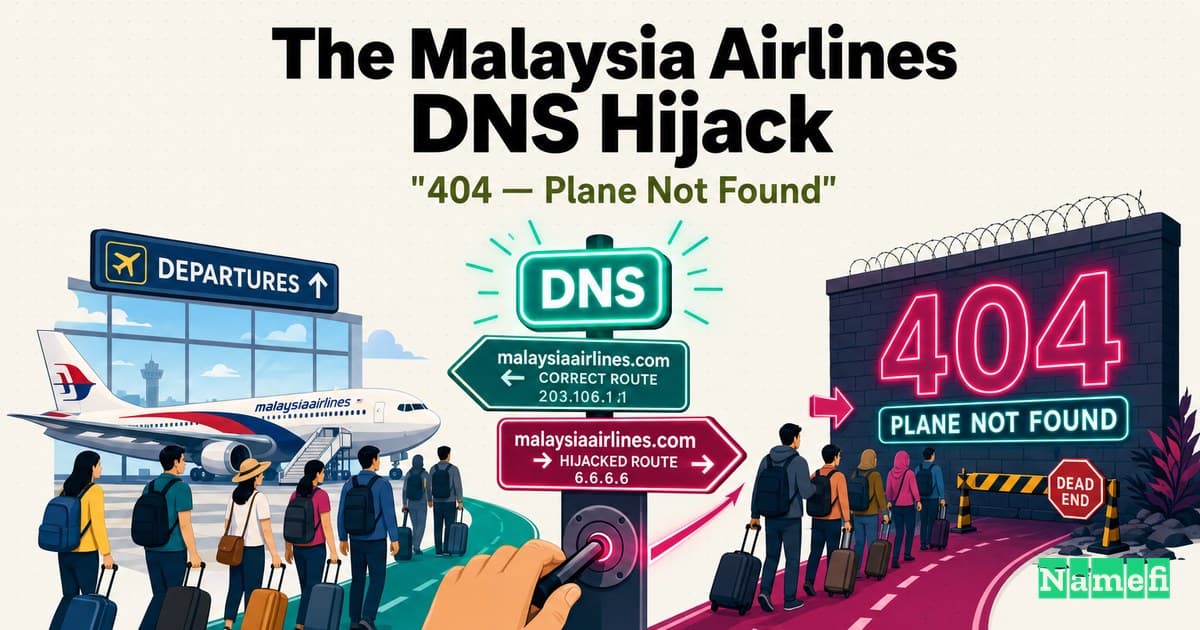
The Malaysia Airlines DNS Hijack: "404 — Plane Not Found"
In January 2015, Lizard Squad hijacked the DNS of malaysiaairlines.com and replaced the airline site with a tuxedo-wearing lizard and the taunt "404 — Plane Not Found." No server was breached — the attackers simply changed where the domain pointed. A Domain Mayday deep-dive into how DNS became the airline's most exposed front door.
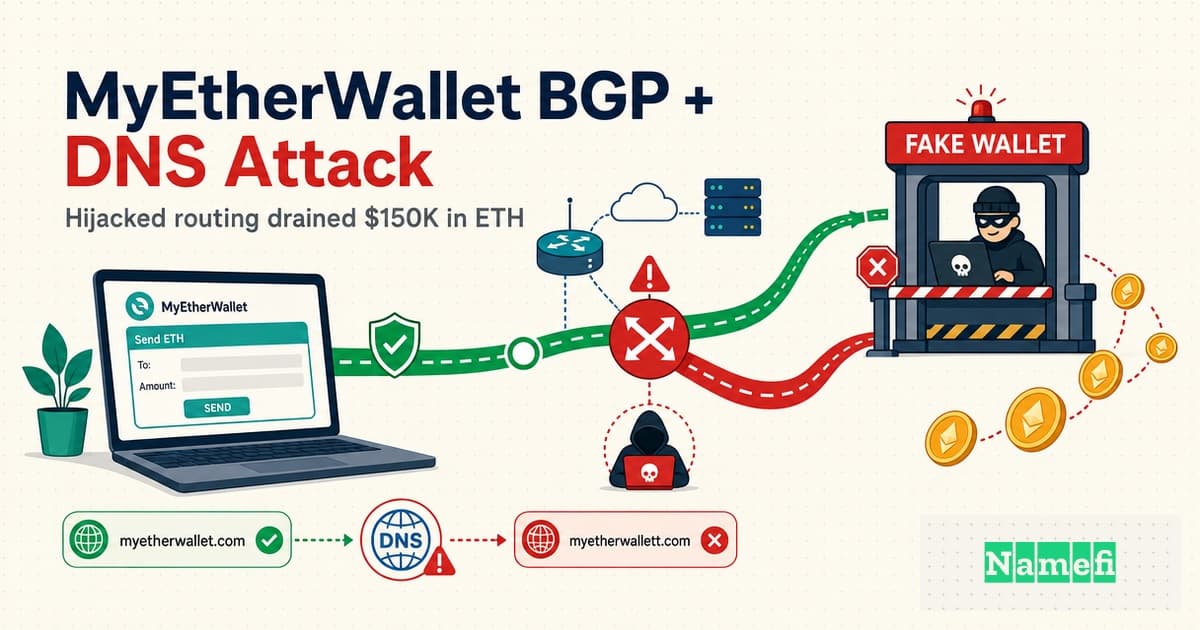
The MyEtherWallet BGP + DNS Attack: How Hijacked Internet Routing Drained $150K in ETH
On April 24, 2018, attackers hijacked the internet routing for Amazon Route 53, poisoned DNS answers for myetherwallet.com, and served a phishing clone behind a self-signed certificate — draining roughly $150,000 in Ethereum. A Domain Mayday deep-dive into why DNS rides on a routing layer that trusts by default.
The Panix.com Domain Hijack: A Fraudulent Transfer of New York's Oldest ISP
In January 2005, panix.com — the domain of New York's oldest commercial ISP — was fraudulently transferred through a reseller account opened with stolen credit-card details. ICANN's review found a failure to obtain express authorization, not a flaw introduced by the then-new transfer policy.
The Perl.com Domain Theft: How a 30-Year-Old Community Home Was Quietly Stolen
In late January 2021, perl.com — a decades-old home of the Perl programming community — was stolen via a registrar-level account compromise, transferred through China, pointed at a malware-linked IP, and listed for $190,000. Here is how it happened, how it was recovered, and what it teaches about registrar account security.
Sea Turtle: The State-Sponsored Campaign That Hijacked DNS to Spy on Governments
How "Sea Turtle," a state-sponsored campaign disclosed by Cisco Talos in 2019, hijacked DNS through registrars, registries, and DNS providers — redirecting governments, ministries, and energy firms to attacker servers, obtaining CA-signed and other certificates for interception, and breaching a national TLD registry.
The Sex.com Heist: A Forged Letter That Stole the Internet's Most Valuable Domain
In 1995 a con man named Stephen Cohen stole sex.com from rightful owner Gary Kremen with a single forged letter to Network Solutions. The years-long fight to win it back ended in a $65 million judgment, a fugitive in Mexico, and a landmark ruling that domains are property.
The SushiSwap MISO Insider Attack: How One Malicious Commit Diverted ~$3M From a Token Auction
In September 2021 an anonymous contractor slipped their own wallet address into SushiSwap's MISO launchpad front-end via a malicious commit, diverting 864.8 ETH (~$3M) from the Jay Pegs Auto Mart auction. A Domain Mayday deep-dive on code supply chains, front-end trust, and what it teaches about verifiable ownership.
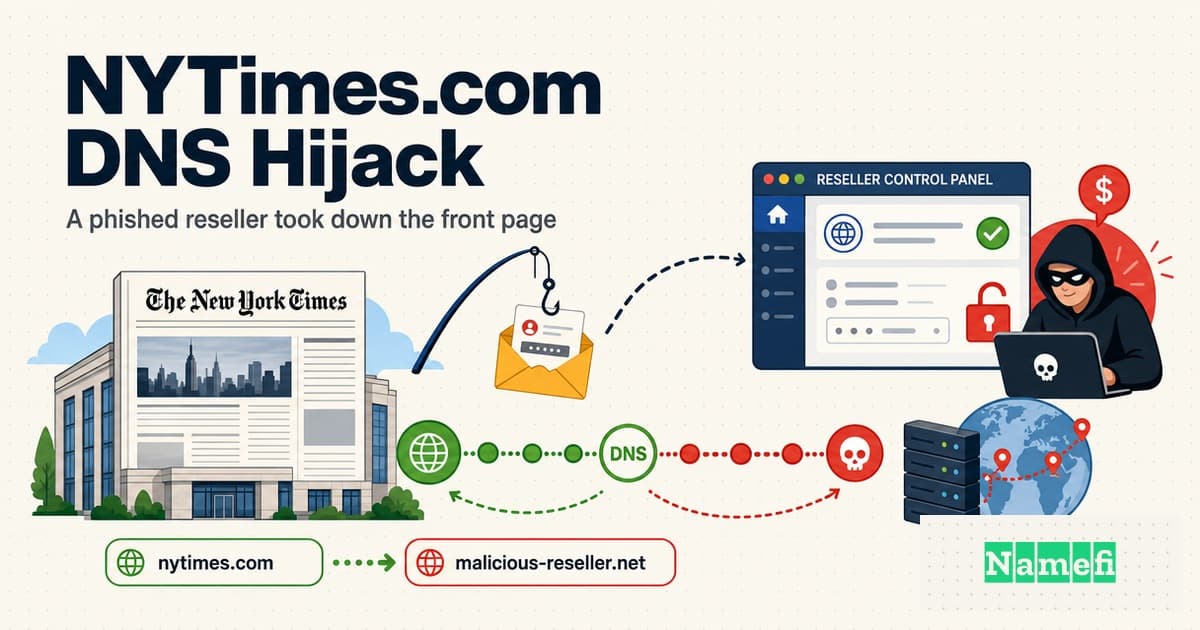
Domain Mayday EP10: How the Syrian Electronic Army Took Down NYTimes.com Through a Phished Reseller
On August 27, 2013, the Syrian Electronic Army phished a Melbourne IT reseller, rewrote the DNS records for nytimes.com and Twitter's domains, and took the New York Times offline for hours. A deep dive into how a registrar-chain weak link became a newspaper's front-door failure — and what registry locks would have changed.
Do Multisig Wallets Actually Improve Security? A Threat-Model View
Multisignature wallets are widely treated as the default secure custody pattern in crypto, but the answer to "do they actually improve security?" depends entirely on the threat model. This post walks through what multisig defeats, what it does not, and where it can make things worse.
DNS over HTTPS vs Enterprise Split-Horizon DNS: A Standoff That Will Not Resolve Itself
DNS over HTTPS (DoH) protects user privacy by encrypting DNS queries inside HTTPS. Enterprise split-horizon DNS relies on the network being able to see those queries. The collision between the two is reshaping how corporate networks, browsers, and operating systems handle name resolution.
Behind the Scenes of the Oct 20, 2025 AWS Outage
A registrar/DNS‑operations perspective on the October 20, 2025 AWS incident, how DNS actually works, why this failure propagated so widely, and what resilient internet teams can do about it.